Malaysia Airlines Data Exposure: What the Amadeus Breach Means and How to Spot Fake Airline Messages
Malaysia Airlines says customer data handled by its booking-system vendor Amadeus between August 2023 and September 2026 may have been exposed. What's known, what scammers may do with real flight details, and the steps worth taking now.

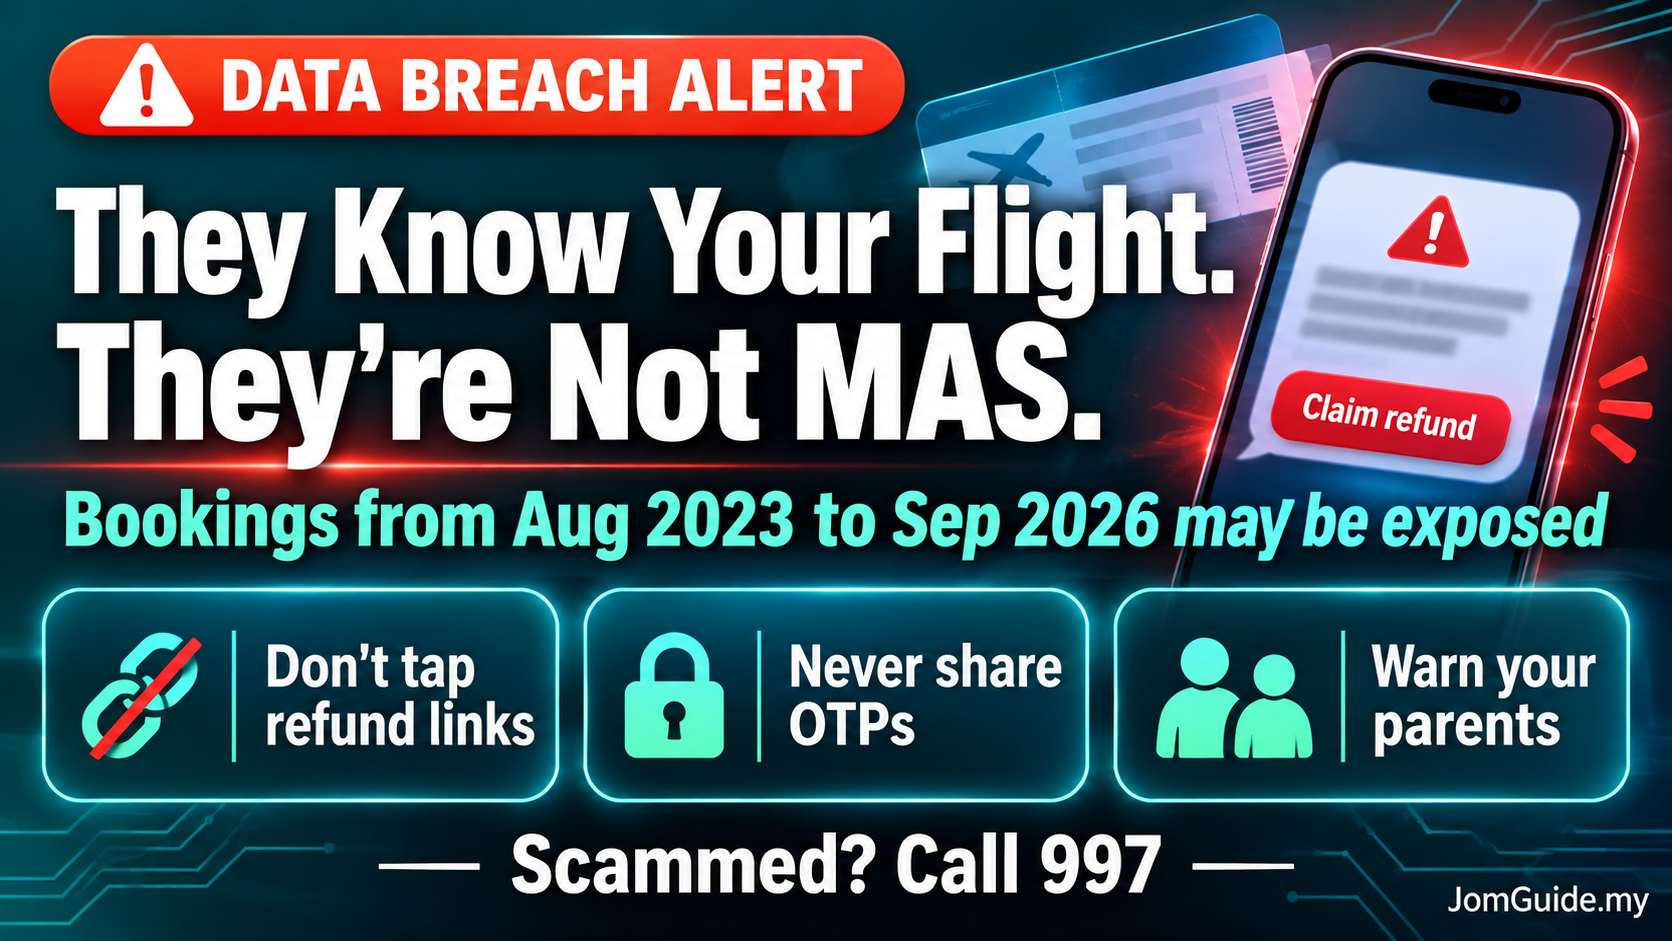
Source: Source: Malaysia Airlines statement (31 Oct 2026) via Malay Mail, VisaVerge, PDP Commissioner Data Breach Notification Guideline
The short version: if you booked or flew with Malaysia Airlines (MAS) between August 2023 and September 2026, your booking details may have been exposed. MAS says its own systems weren't breached and there is no evidence so far that financial information was accessed. The real risk right now isn't your bank card. It's scammers who know your actual flight history.
Information as of 2 November 2026. Follow MAS's official updates for anything new.
What happened
- The breach was at Amadeus, the third-party technology provider behind airline reservations, ticketing and check-in.
- MAS said on 31 October that customer information processed through Amadeus between August 2023 and September 2026 may have been exposed. Its own IT systems were not compromised, and there is no evidence financial information was accessed.
- Several other airlines are affected, including Japan Airlines, ANA, Korean Air, Asiana and Cathay Pacific. Reports say the intruders used login credentials for an account in Amadeus's system to view booking records.
What data may be involved
MAS hasn't said how many customers are affected or which data types were involved. Other airlines' disclosures give a sense of the range:
| Airline | Disclosed so far |
|---|---|
| Japan Airlines | Names, booking codes and flight details for about 92,000 customers; about 2,000 also had passport numbers, frequent-flyer numbers, emails and phone numbers exposed |
| Asiana | Booking information; payment data sits on a separate system and wasn't exposed |
| Korean Air | Booking reference numbers confirmed; other data still being reviewed |
| MAS | No details yet; no evidence financial data was accessed |
The safe assumption is that your name, booking reference, travel dates and routes may already be in someone else's hands.
How scammers could use it
Real flight details make fake messages very convincing. Watch for:
- Fake refunds: "Your KL–Taipei flight in March 2025 is eligible for a refund. Click here to enter your bank details."
- Fake schedule changes: "Your flight next month has been rescheduled. Please verify your identity."
- Fake miles offers: "Your Enrich miles are about to expire. Log in to redeem."
- Fake customer service calls: the caller quotes your real flight and date, then asks for an OTP or password.
Remember: someone knowing your flight doesn't mean they're MAS.
Five things to do now
- Don't tap links in messages. Check any refund, rebooking or miles notice yourself in the official MAS app or website.
- Never share OTPs, passwords or card details. An airline doesn't need your OTP to process a refund.
- Change your Enrich password, especially if you reuse it elsewhere. This is a precaution; MAS hasn't said Enrich passwords were exposed.
- Warn older family members first. If you've booked flights for your parents, it's their details at stake, and they are the most likely to trust a caller who knows their itinerary.
- If you've been scammed, call NSRC at 997 immediately, then your bank and the police. See our guide, Scammed in Malaysia? Do These 3 Things First.
JomGuide's advice: if you do only one thing, warn your parents. They are the most likely to get the "customer service" call and the least likely to check the app themselves.
Will MAS contact me?
So far MAS has only said it will share updates as more information becomes available. It hasn't said whether it will notify customers individually.
Under the Personal Data Protection Commissioner's Data Breach Notification Guideline, when a breach is likely to cause "significant harm", the data controller must:
- notify the Commissioner within 72 hours, and
- notify affected individuals directly within 7 days of that, explaining what happened, the likely consequences and what they should do.
The guideline's examples of significant harm include data that could enable identity fraud and breaches affecting more than 1,000 people. A public notice is allowed where direct notification isn't practicable.
JomGuide's view: an airline holds contact details for every passenger. It should notify each affected customer directly and spell out exactly what was exposed, not rely on a public statement alone.
Until then, you can ask MAS through the official customer service channels in its app or website whether your booking was affected.
FAQ
Was my card information exposed?
MAS says there is no evidence financial information was accessed. Anyone asking for your card number or OTP in the name of a refund is a scammer.
I flew other airlines, not MAS. Should I worry?
The incident affects several Amadeus customers, including JAL, ANA, Korean Air, Asiana and Cathay Pacific. If you've flown with them, stay alert too.
Should I replace my passport?
MAS hasn't said passport numbers were exposed or advised anyone to replace a passport. Watch for further updates.
What should I do with a suspicious message?
Don't reply or tap any link; check in the official app instead. If you've already sent money or details, call 997 right away.
Useful? Forward it to someone who needs it.
Malaysian policy and hot topics, 2–3 items a week, each with a one-line “so what”.
Related articles
More in Jom Trending-
Malaysia Fuel Prices 12–18 November 2026: RON97 Down 50 Sen to RM4.20, RON95 RM3.87, Diesel RM4.87, BUDI95 Still RM1.99
-
TuJu Now Sends You to Google Maps: The Latest on the Waze Ban, and No, the Public Isn't Banned
-
Malaysia Fuel Prices 5–11 November 2026: All Down, RON95 RM4.27, RON97 RM4.70, Diesel RM5.12, BUDI95 Still RM1.99